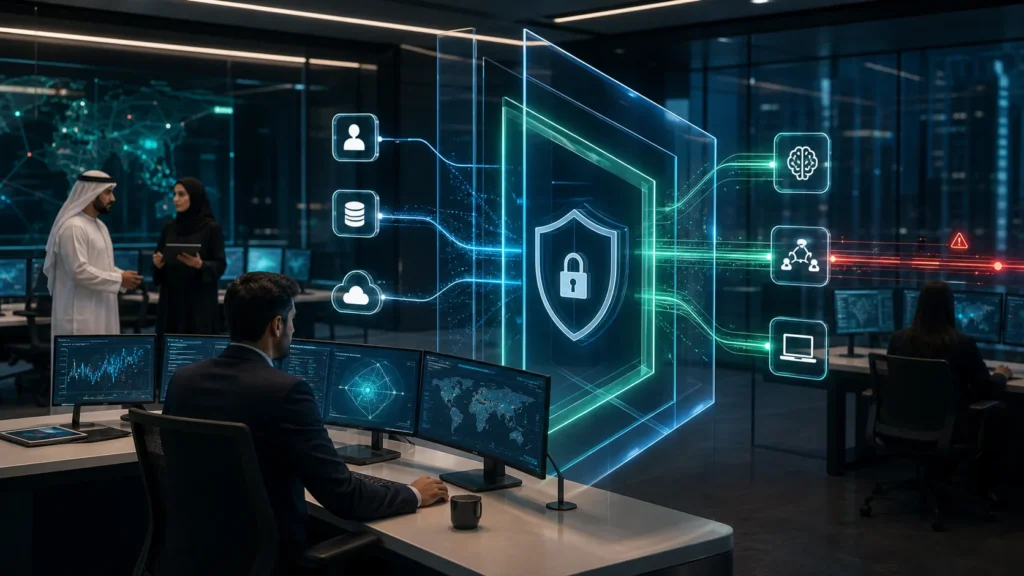
AI does not create the need for cybersecurity readiness. It reveals whether the foundation was ready in the first place. When information becomes easier to find, summarize, and automate, weak controls become business risks faster.
Strong access control is the foundation for safe AI use across cloud and business systems.
Classification, retention, and sharing rules help prevent accidental exposure.
Monitoring should focus on behaviors that matter, not noisy alerts that no one investigates.
Backup and response plans must be tested before the business depends on them.
AI changes visibility
A traditional file search may return a list of documents. An AI assistant may summarize those documents, connect ideas across them, and make sensitive information easier to understand. That can be extremely useful when access is correct and risky when permissions are loose.
Organizations preparing for AI should therefore review document sharing, group membership, guest access, privileged accounts, and inactive users. The goal is not to slow adoption. It is to make sure AI sees only what the user should already be allowed to use.
Security must follow the workflow
AI-connected businesses often join email, chat, documents, CRM, finance, operations, and support systems. A security design that only protects the perimeter will miss how work actually happens. Controls need to follow identity, data, devices, and applications.
This usually means conditional access, endpoint management, multi-factor authentication, role-based access, audit logs, and clear incident response paths. These are familiar controls, but AI raises the value of implementing them consistently.
Governance should be practical
Governance becomes useful when teams understand what is allowed, what needs approval, and what must never happen. Long policy documents are less effective than clear use-case rules, data categories, access patterns, and escalation routes.
For example, a company might allow AI summarization of public sales material, restrict AI use on HR documents, and require review before connecting AI to customer financial records. Practical boundaries help users move without guessing.
Readiness is ongoing
AI capabilities will keep changing, so readiness cannot be a one-time checklist. Security posture, permissions, prompts, connectors, and user behavior should be reviewed regularly. Managed monitoring and periodic assessments help keep the environment aligned as usage expands.
The best security programs are visible without being disruptive. They give leaders confidence that innovation and control can move together.
A 90-day execution view
Days 1-30: clarify the real operating problem
The first month should be spent narrowing the topic into a business workflow that can be owned, measured, and improved. This is where leadership defines the current friction, the affected teams, the systems involved, and the risk of doing nothing. For cybersecurity readiness for ai-connected businesses, that means resisting the temptation to start with a broad transformation label and instead choosing a practical operating question.
Discovery should include business owners, IT, security, data stakeholders, and the users who live with the process every day. Their input usually reveals constraints that are invisible in a strategy deck: manual rework, unclear approvals, duplicate data, licensing gaps, support noise, or permissions that no longer match how the organization works.
Days 31-60: build a controlled first release
The second month should produce something useful but contained. A controlled release may be a decision model, automation workflow, cloud landing pattern, security baseline, data layer, or managed-service operating rhythm. The point is to put the idea into a realistic environment with real users, real permissions, and a support path.
This is also where quality gates matter. The team should check security, privacy, data reliability, user experience, reporting, and fallback procedures before expanding access. A first release that is small and dependable will create more confidence than a large release that is hard to explain.
Days 61-90: measure, improve, and decide what scales
The third month should focus on evidence. Did the workflow reduce effort, risk, delay, cost, or uncertainty? Did users adopt it without constant reminders? Did the business owner receive clearer information? Did IT and support teams gain better control? These answers decide whether the initiative should scale, pause, or change direction.
At this stage, the organization should document what can be reused. Identity patterns, integration methods, data definitions, templates, runbooks, and support lessons are often more valuable than the first use case itself because they make the next initiative faster and safer.
Governance and measurement
Governance should be light enough to keep momentum but clear enough to prevent confusion. The essentials are ownership, access rules, change control, support routes, security review, and a simple decision log. When those basics are visible, teams can move faster because they do not need to renegotiate every choice from scratch.
Measurement should combine operational and human signals. Useful measures may include cycle time, incident volume, handoff reduction, data-quality exceptions, adoption rate, avoided rework, support effort, and leadership confidence. The best metric is the one that proves a real workflow became easier, safer, faster, or more reliable.
Questions leaders should ask
- Which business decision, workflow, or risk should improve first?
- Who owns the outcome after the technology work is delivered?
- Which data, access, and support assumptions need to be validated early?
- What would make users trust the new process enough to change behavior?
- How will leadership know whether the first release is worth expanding?
Common mistakes to avoid
- Starting with a tool selection before agreeing the operating problem.
- Treating governance as a final review instead of a design input.
- Ignoring adoption, training, support, and ownership until go-live.
- Measuring activity instead of business improvement.
- Scaling a weak first version before the feedback loop is working.
AI readiness and security readiness should be planned together. The safest AI program is the one built on clear identity, clean permissions, and monitored usage.
Practical next steps
- Review identity, MFA, and privileged-account controls.
- Audit document sharing and sensitive data locations.
- Define approved AI use cases and restricted data categories.
- Check endpoint, email, and cloud security baselines.
- Test backup and response procedures before scaling AI use.
Where this connects
For organizations reviewing their next technology priorities, this topic connects directly with Vivolution services and solution areas:
Teams that want to move carefully can begin with a focused assessment, a small production use case, and a clear roadmap for security, cloud, data, and managed operations.