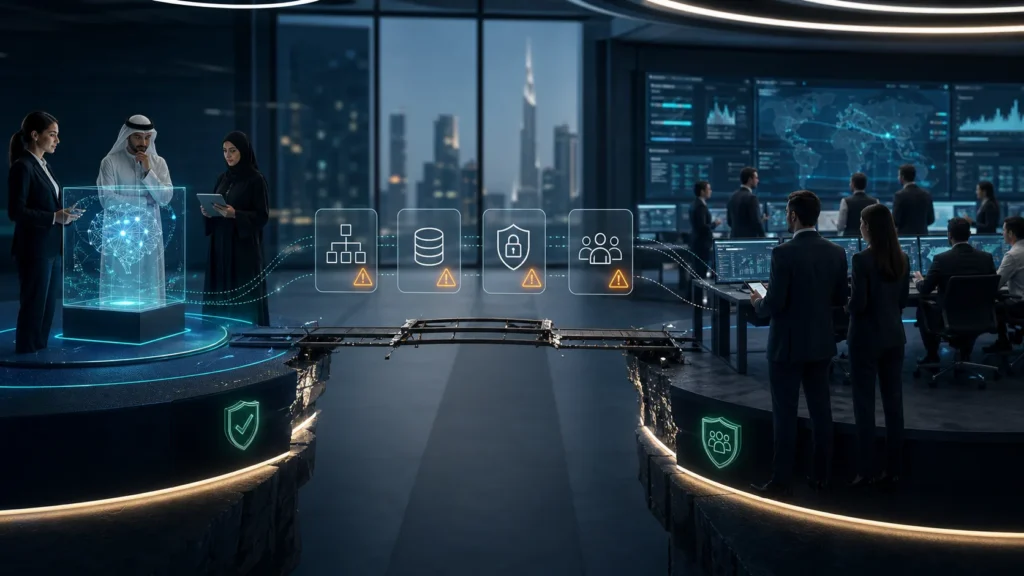
An AI pilot can impress a leadership team in a demo and still fail quietly three months later. The gap is rarely the idea. It is the missing bridge between prototype behavior and day-to-day business operations.
A pilot needs a business owner, a technical owner, and a support model before it becomes operational.
If inputs are inconsistent, unclassified, or hard to access, the AI experience quickly loses credibility.
Security, privacy, logging, and permission design cannot be added casually at the end.
Users need training, feedback routes, and a reason to trust the workflow.
The demo is not the operating model
A pilot usually works in a controlled environment: selected users, curated data, direct attention from the project team, and a narrow use case. Production is different. More users appear, edge cases multiply, permissions matter, service levels become visible, and the business expects support when something breaks.
This is why an AI initiative should define its operating model early. Who approves new use cases? Who owns prompts, datasets, connectors, and access policies? Who reviews outputs for quality? Who decides when the tool is retired, redesigned, or expanded?
Data readiness is not optional
AI systems amplify the condition of the information they are given. If documents are duplicated, permissions are messy, customer records are inconsistent, or process data is incomplete, the pilot may still look exciting but production will feel unreliable.
The strongest AI roadmaps spend time on classification, retention, knowledge structure, integration, and master data decisions. This does not mean every system must be perfect. It means the first production use cases should be matched to data that is trustworthy enough for the decision being supported.
Security has to shape the design
AI changes the risk profile of ordinary business data because it makes information easier to retrieve, summarize, and combine. A document that was technically accessible but practically hidden can become highly visible once AI search and copilots are introduced.
Before scaling, organizations should review identity controls, conditional access, document permissions, endpoint posture, audit logging, and data loss prevention. This is a practical business safeguard, not a blocker. Good controls let teams adopt AI with more confidence.
Adoption is a product discipline
A pilot often depends on curious early adopters. Production depends on ordinary users who have targets, habits, deadlines, and limited patience. If the AI workflow adds another place to check, another confusing approval, or unclear output quality, people will return to the old process.
Treat the workflow like a product. Start with clear jobs to be done, user feedback, usage analytics, support content, and a release rhythm. The goal is not to tell people that AI is useful; it is to make the useful path easier than the old one.
A 90-day execution view
Days 1-30: clarify the real operating problem
The first month should be spent narrowing the topic into a business workflow that can be owned, measured, and improved. This is where leadership defines the current friction, the affected teams, the systems involved, and the risk of doing nothing. For why ai projects fail after the pilot stage, that means resisting the temptation to start with a broad transformation label and instead choosing a practical operating question.
Discovery should include business owners, IT, security, data stakeholders, and the users who live with the process every day. Their input usually reveals constraints that are invisible in a strategy deck: manual rework, unclear approvals, duplicate data, licensing gaps, support noise, or permissions that no longer match how the organization works.
Days 31-60: build a controlled first release
The second month should produce something useful but contained. A controlled release may be a decision model, automation workflow, cloud landing pattern, security baseline, data layer, or managed-service operating rhythm. The point is to put the idea into a realistic environment with real users, real permissions, and a support path.
This is also where quality gates matter. The team should check security, privacy, data reliability, user experience, reporting, and fallback procedures before expanding access. A first release that is small and dependable will create more confidence than a large release that is hard to explain.
Days 61-90: measure, improve, and decide what scales
The third month should focus on evidence. Did the workflow reduce effort, risk, delay, cost, or uncertainty? Did users adopt it without constant reminders? Did the business owner receive clearer information? Did IT and support teams gain better control? These answers decide whether the initiative should scale, pause, or change direction.
At this stage, the organization should document what can be reused. Identity patterns, integration methods, data definitions, templates, runbooks, and support lessons are often more valuable than the first use case itself because they make the next initiative faster and safer.
Governance and measurement
Governance should be light enough to keep momentum but clear enough to prevent confusion. The essentials are ownership, access rules, change control, support routes, security review, and a simple decision log. When those basics are visible, teams can move faster because they do not need to renegotiate every choice from scratch.
Measurement should combine operational and human signals. Useful measures may include cycle time, incident volume, handoff reduction, data-quality exceptions, adoption rate, avoided rework, support effort, and leadership confidence. The best metric is the one that proves a real workflow became easier, safer, faster, or more reliable.
Questions leaders should ask
- Which business decision, workflow, or risk should improve first?
- Who owns the outcome after the technology work is delivered?
- Which data, access, and support assumptions need to be validated early?
- What would make users trust the new process enough to change behavior?
- How will leadership know whether the first release is worth expanding?
Common mistakes to avoid
- Starting with a tool selection before agreeing the operating problem.
- Treating governance as a final review instead of a design input.
- Ignoring adoption, training, support, and ownership until go-live.
- Measuring activity instead of business improvement.
- Scaling a weak first version before the feedback loop is working.
The right question is not whether an AI pilot can work. The right question is whether the organization is ready to operate, govern, support, and improve it after the demo.
Practical next steps
- Write the production owner names before the pilot begins.
- Test the pilot with realistic permissions and imperfect data.
- Define security, logging, and support expectations early.
- Create a feedback loop for users and business reviewers.
- Move one workflow into production before starting five new pilots.
Where this connects
For organizations reviewing their next technology priorities, this topic connects directly with Vivolution services and solution areas:
Teams that want to move carefully can begin with a focused assessment, a small production use case, and a clear roadmap for security, cloud, data, and managed operations.